

Blind and Delegated Quantum Computation
Delegated quantum computation lets a computationally limited client ask a quantum server to perform a computation. Blind quantum computation adds a privacy guarantee: the server learns no more about the client’s input, algorithm, or output than a declared leakage function permits. Verifiable delegation adds an integrity guarantee: a cheating server can make the client accept an incorrect result only with bounded probability.
These are distinct properties. A protocol may verify a public computation without hiding it, or hide a computation without detecting a deliberately wrong result. Neither property forces the server to answer. A malicious server can usually delay, refuse service, or cause an abort.
The central example is prepare-and-send universal blind quantum computation (UBQC): a client hides measurement instructions with random qubit phases and random outcome flips. Verification adds a separate mechanism for detecting incorrect computation. We compare the assumptions needed when a client can prepare qubits, measure them, or communicate only classically.
Required background. Circuit computation describes the delegated task; graph states and teleportation explain the quantum resource and feed-forward. Trace distance measures distinguishability of real and ideal outputs.
Delegated channels and security guarantees
Section titled “Delegated channels and security guarantees”Let Alice be the client and Bob the quantum server. Alice supplies a computation , an input or quantum state , and a security parameter . Bob supplies quantum processing, memory, measurement, and communication resources. At the end Alice obtains one of:
- a classical result ;
- a quantum output register, usually still encrypted under a Pauli key;
- a rejection symbol .
The ideal computation is a channel . For a unitary task,
For sampling, measurement, or noisy-channel tasks, should be read as the complete intended channel, including the declared measurement and classical output. Stating only a circuit is not enough. One must also specify which party supplies and receives each input and output register, which transcript fields are public, what Bob may retain, and whether Alice accepts approximate output.
Four guarantees that should not be merged
Section titled “Four guarantees that should not be merged”An honest execution should be correct. For a protocol without abort, a composable quantum-output criterion compares the implemented channel with the intended channel even on an input entangled with a reference :
for every allowed input and reference. Including matters: correct reduced output states alone need not preserve their correlations. An aborting implementation must additionally specify the accepted branch and abort behavior in its ideal comparison.
If the protocol includes tests, honest noise may make Alice reject. Its completeness error is
Blindness concerns Bob’s information, not Alice’s output accuracy. Write for Bob’s final quantum system together with the entire classical transcript visible to him. Let be explicitly permitted leakage, such as a padded upper bound on circuit size. An information-theoretic blindness statement has the form
For each server strategy, the simulator has the allowed leakage and the server’s permitted initial side information, but not Alice’s private data. The displayed expression suppresses these strategy and side-information arguments; a full definition includes them and any external reference. If it can reproduce Bob’s real view, Bob cannot extract extra information from that view. Perfect blindness has ; statistical blindness allows a small trace-distance error.
Computational protocols use a different claim. For every efficient quantum distinguisher and security parameter ,
provided the two delegated tasks have the same permitted leakage and the declared post-quantum assumption holds. Calling this “unconditional” would be wrong even if the underlying quantum computation is ideal.
Verifiability concerns accepted wrong outputs. For a deterministic classical task with answer and accepted tolerance , a direct condition is
For a sampling task, there is no single correct sample : the target is an output distribution, or a task-specific relation. Checking that each answer lies in the distribution’s support cannot verify its probabilities. For quantum output, the ideal resource instead says that Alice receives either the correct output, up to the stated error, or . This formulation avoids pretending that one can inspect an unknown quantum state and compare it with a classical answer sheet.
Composability and availability
Section titled “Composability and availability”A guarantee about one isolated run need not imply security when its output is reused or sessions interact. Dunjko, Fitzsimons, Portmann and Renner (2014) give a composable framework and explain why local blindness and ordinary local verifiability alone are not a general composition theorem. Their independent-verifiability condition restricts how acceptance can depend on private data.
Once complete components are proved close to compatible ideal resources, a composition theorem can add their distinguishing errors. For example, replacing a delegated-computation resource with error and an authenticated channel with error gives a bound in a framework supporting these substitutions. One cannot obtain merely by adding separately named correctness, blindness, completeness and trap-failure numbers.
None of these security properties guarantees availability. Bob can stop sending messages or force tests to fail. Redundant providers and service-level mechanisms may improve availability, but they do not turn cryptographic verification into a liveness theorem.
Trust and Capability Models
Section titled “Trust and Capability Models”There is no single “minimal client” without a trust model. Preparing one of a few qubit states, measuring incoming photons, keeping two servers isolated, and running lattice-based cryptography are incomparable resources.
| Client model | Trusted ability | Additional premise |
|---|---|---|
| Prepare and send | prepare hidden qubit states | quantum link and characterized source |
| Receive and measure | measure incoming systems | isolated laboratory; protocol-specific detector model |
| Remote state preparation | measure a flying partner | interface and heralding model |
| Small quantum verifier | encode or measure a small register | authentication or hidden-test construction |
| Classical, multiple servers | classical control | separated entangled servers cannot communicate as excluded by the proof |
| Classical, one server | classical cryptography | named post-quantum hardness assumptions |
“Device-independent” must also be qualified. A receive-and-measure protocol may remove trust in a client measurement model for a particular privacy claim, while a multi-prover protocol may certify behavior from nonlocal correlations. Neither label means that timing, laboratory isolation, randomness, classical software, and all interfaces can be ignored. The declared boundary matters more than the adjective.
Universal Blind Quantum Computation
Section titled “Universal Blind Quantum Computation”The UBQC protocol of Broadbent, Fitzsimons and Kashefi (2009) is an example of information-theoretic blindness with a weak quantum client. It uses measurement-based quantum computation, but only a small amount of that model is needed here.
Minimal measurement-based mechanics
Section titled “Minimal measurement-based mechanics”Bob prepares a universal graph-state geometry, such as a brickwork state, by entangling qubits with controlled- gates. A single-qubit measurement basis in the equatorial plane is
Measuring successive graph vertices teleports logical information through the resource while applying gates determined by the measurement angles. Outcomes are random, so later angles must depend on parities of earlier outcomes. For the algorithmic angle , write the corrected angle as
where and are protocol-defined parities of earlier decoded outcomes. The graph’s flow or generalized flow determines those dependencies. The full measurement-pattern model, including branch maps, byproduct propagation, flow or gflow determinism, and compilation boundaries, belongs to Measurement-Based Quantum Computation; here the issue is how to conceal the pattern from Bob.
Protocol skeleton
Section titled “Protocol skeleton”For each resource qubit , Alice samples
where
The protocol proceeds as follows.
- Alice sends Bob independently prepared states . A private classical input can be compiled into the initial measurement pattern. Quantum inputs require the protocol’s additional input-encryption procedure; equatorial resource preparation alone does not encode an arbitrary unknown input.
- Bob entangles the qubits according to the public, usually padded, resource graph.
- Before measurement , Alice computes from earlier decoded outcomes and sends
- Bob measures in the basis and returns the raw bit .
- Alice removes the outcome pad,
and uses to compute future corrections. 6. Alice decodes the classical output or removes the final Pauli key from a quantum output.
Why both masks matter
Section titled “Why both masks matter”Bob receives an ensemble whose average state is maximally mixed:
The roots of unity sum to zero. Moreover, measuring at physical angle is equivalent to measuring an unrotated state at angle
Adding swaps the labels of the two basis vectors, so encrypts the outcome without changing the logical operation after Alice decodes it.
The marginal average is not enough because Bob later receives , which is correlated with the prepared qubit. Consider one nonadaptive instruction with fixed target angle . For any announced , the two equally likely possibilities are
The corresponding states are orthogonal. Thus
The joint state of the instruction and qubit is independent of . If Alice omitted , the qubit conditioned on would instead be the pure state . Targets and would then be perfectly distinguishable, despite identical qubit marginals and uniformly random instructions. Exercise 8 constructs Bob’s measurement.
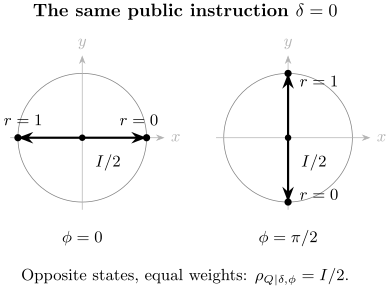
Condition on the same public instruction . For the unknown outcome pad selects the two eigenstates; for it selects the two eigenstates. Each equal mixture is , the center of the Bloch disk. The full adaptive malicious-server proof also covers entangling operations, earlier messages and retained ancillas; this one-round calculation explains its masking mechanism.
A masked-angle example
Section titled “A masked-angle example”Suppose
Then
If Alice sampled and , she sends
Bob sees the ordinary-looking instruction . If he reports , Alice records . The arithmetic does not reveal because Bob does not know the phase and outcome masks or the corrected feed-forward parities.
What UBQC still leaks
Section titled “What UBQC still leaks”The standard construction does not make the interaction invisible. Unless it is padded and scheduled independently of private data, Bob may learn:
- the resource-graph geometry and an upper bound on width and depth;
- the number and timing of measurements;
- which messages are quantum and which are classical;
- loss, retry, and abort patterns;
- the output type or number of output qubits;
- network metadata and client identity.
A universal brickwork graph hides which gates are active within the graph, but its dimensions can reveal a circuit-size bound. Padding hides size only within an anonymity set and adds qubits, time, and noise. The leakage function must list what remains; “the server learns nothing” is incomplete.
From Blindness to Verifiability
Section titled “From Blindness to Verifiability”Blindness can make tests indistinguishable from computation. This lets Alice hide checks among useful operations so that Bob cannot target only the data.
Hidden traps and dummies
Section titled “Hidden traps and dummies”In the trap-based construction of Fitzsimons and Kashefi (2017), Alice embeds vertices with known deterministic outcomes. Dummy qubits isolate selected trap qubits from the computation graph. Random preparation and hidden placement prevent Bob from knowing which vertices are traps.
An honest execution produces the expected trap outcomes, apart from the declared physical-noise model. A malicious deviation large enough to corrupt the computation has a protocol-dependent probability of disturbing a hidden trap. Repetition, graph coloring, or encoded constructions can reduce the soundness error while retaining polynomial overhead.
For intuition only, if each independent repetition detects a fixed attack with probability at least , then repetitions miss it with probability at most
Real security proofs cannot assume that a quantum adversary attacks rounds independently. They reduce arbitrary coherent deviations to a form for which the hidden test structure gives a bound. The toy expression is useful for planning, not for replacing that reduction.
Quantum authentication
Section titled “Quantum authentication”Another family authenticates the quantum data. Alice encodes the input using a secret key, for example through a random Clifford or signed polynomial code. Bob computes on authenticated data using prescribed gadgets. At the end Alice checks the authentication syndrome and accepts only if it is valid.
Authentication hides the data when combined with a quantum one-time pad and detects tampering, but its client operations, ancillary states, interaction, and fault-tolerance requirements differ from trap-based UBQC. Aharonov et al. (2017) develop authentication-based interactive proofs. Stabilizer codes provide useful encoding tools; cryptographic authentication additionally uses a secret key and a bound against adversarial tampering.
Computation rounds and test rounds
Section titled “Computation rounds and test rounds”Some protocols randomly interleave computation rounds with efficiently checkable test rounds. If the protocol’s hiding mechanism makes the two types indistinguishable to Bob, failures in the tests constrain his ability to corrupt the computation unnoticed. The inference must include the test-sampling rule, tolerated honest noise, confidence procedure, and a proof relating test statistics to accepted computation, including coherent attacks.
Passing a few stabilizer checks is not automatically universal verification. The inference depends on the protocol theorem and its noise assumptions.
Classical Clients and Multiple Servers
Section titled “Classical Clients and Multiple Servers”Removing the client’s last trusted quantum operation is conceptually valuable, but it moves the burden elsewhere.
Two or more noncommunicating servers
Section titled “Two or more noncommunicating servers”A classical verifier can interact with entangled quantum provers that are prevented from communicating during the protocol. Nonlocal games and rigidity theorems constrain the provers’ effective measurements and shared state. This supports classical control and verification of general quantum computations, and variants can provide blindness.
The isolation assumption is cryptographic, not cosmetic. If the servers share the verifier’s questions during the live protocol, the soundness argument may collapse. Space-like separation is one route, but practical deployments must also control hidden radio, optical, timing, and supply-chain channels. A two-server protocol does not become a one-server protocol merely because both machines are operated by the same provider.
Reichardt, Unger and Vazirani (2013) use rigidity to obtain classical verification with entangled, separated provers. Privacy is an additional protocol property, not a consequence of rigidity alone.
One server under computational assumptions
Section titled “One server under computational assumptions”Mahadev’s 2018 protocol showed that a probabilistic polynomial-time classical verifier can verify general quantum computation with one quantum prover under post-quantum cryptographic assumptions related to learning with errors (LWE). Trapdoor claw-free function families let the verifier enforce measurements in incompatible bases without possessing a qubit.
This changes the security category:
- soundness is computational rather than information-theoretic;
- the prover is assumed unable to break the selected post-quantum primitive;
- key generation, parameter selection, classical cryptography, and protocol compilation enter the trusted base;
- asymptotic polynomial overhead may still be impractical at useful sizes.
Classical verification does not automatically hide the circuit or input. Blind delegation requires a protocol and proof that explicitly provide privacy, or an additional encryption layer. “Mahadev-style” is not a complete security specification.
Measurement-only clients
Section titled “Measurement-only clients”In a measurement-only protocol, Bob sends quantum systems and Alice performs single-qubit measurements. Morimae and Fujii (2013) use the no-signaling principle to protect Alice’s choices in models where her laboratory does not leak the basis or outcome. This may be easier than preparing calibrated states on some optical platforms.
The direction of the quantum channel reverses the implementation risks. Alice must address detector behavior, wavelength and mode dependence, loss, malicious bright-light inputs, and basis-dependent side channels. Protocols also differ in whether Alice’s measurement device is trusted, characterized, or covered by a device-independent claim. Those variants should not be merged.
Quantum Homomorphic Encryption
Section titled “Quantum Homomorphic Encryption”Blind interactive computation and quantum homomorphic encryption (QHE) solve related but different tasks. In QHE, a client encrypts quantum data, a server evaluates a circuit on the ciphertext, and the client decrypts the result. A compact scheme asks that decryption cost depend on the security parameter and output size rather than on the full evaluated circuit.
The quantum one-time pad encrypts an -qubit state as
Averaging over secret keys gives
Clifford gates transform Pauli keys into new Pauli keys, so Alice can update the encryption classically. Non-Clifford gates are harder: they require interaction, auxiliary states, gate gadgets, or classical homomorphic encryption of key-dependent corrections. This is one reason -gate count or -depth appears in resource bounds.
Yu, Pérez-Delgado and Fitzsimons (2014) establish a no-go boundary. Perfectly information-theoretic, deterministic fully homomorphic quantum encryption for arbitrary circuits incurs exponential overhead under the standard compactness setting. Schemes such as Broadbent and Jeffery (2015), and restricted circuit families, avoid that conclusion by changing the security or functionality assumptions. The no-go result does not forbid interactive blind computation, approximate tradeoffs, or QHE for limited gate sets.
Adaptive communication and physical noise
Section titled “Adaptive communication and physical noise”Measurement dependencies determine how much computation can be batched. In a deliberately serial latency model,
Here is a round-trip delay and the local times exclude that delay. Pipelining can overlap these terms, so the sum is not a general lower bound. An adaptive layer cannot start before the outcomes needed to determine its angles arrive. Padding, hidden traps and error correction increase both graph size and communication demands. The relevant rate is accepted computations per wall-clock time, with failed attempts included.
Honest noise and adversarial deviations
Section titled “Honest noise and adversarial deviations”Cryptographic and physical errors play different roles. A trap should detect a malicious deviation, but honest noise can also trigger it. Raising the test tolerance improves completeness and may weaken soundness unless the proof accounts for the noise. Postselecting every inconvenient event can open a security loophole and destroy scalability.
Fault-tolerant blind computation combines encrypted or hidden logical operations with quantum error correction. Topological measurement-based constructions can hide a computation within a three-dimensional cluster-state architecture. Authentication-code protocols can incorporate fault-tolerant gadgets. In either case, one must jointly track:
These terms are not interchangeable. A low logical error rate does not prove blindness, and a strong trap bound does not correct decoherence. Threshold Theorem explains when logical error can be suppressed; Resource Estimation connects physical qubits, factories, cycles and decoding to runtime.
Implementation Security
Section titled “Implementation Security”A proof applies to an interface model. Hardware and software must implement that interface closely enough that excluded degrees of freedom do not carry the secret.
State-preparation leakage
Section titled “State-preparation leakage”The states labeled must differ only in the intended qubit degree of freedom. Angle-dependent spectra, emission time, pulse energy, spatial mode, multiphoton probability, or device memory can reveal . The relevant object is Bob’s full emitted state , including side-channel system , not an ideal qubit alone.
Malicious inputs to the client
Section titled “Malicious inputs to the client”Receive-and-measure and remote-state-preparation clients should constrain wavelength, intensity, timing, and spatial mode. Otherwise Bob may probe the measurement setting with reflected light, exploit detector nonlinearities, or inject systems outside the proof’s dimension. Optical isolators, filters, power monitoring, randomized calibration, and explicit abort rules belong to the security design.
Loss and selective reporting
Section titled “Loss and selective reporting”If a party may declare “no detection” after learning a hidden variable, postselected data can be biased. The protocol must specify which losses are trusted, when a herald is committed, whether retries reuse secrets, and how acceptance depends on missing events. Loss tolerance is a theorem property, not an automatic benefit of using photons.
Randomness and key lifecycle
Section titled “Randomness and key lifecycle”Phase masks, outcome pads, trap locations, challenge bits, and cryptographic keys require suitable private randomness. Reusing across sessions creates transcript correlations. Keys and decoded feed-forward data should be domain-separated by session, authenticated in transit, and erased according to the threat model. Quantum Randomness explains entropy certification and extraction.
Metadata, compiler, and abort leakage
Section titled “Metadata, compiler, and abort leakage”A private source program can leak before the quantum protocol begins. Compiler branching, graph dimensions, cache and queue behavior, message timing, retry counts, and distinct error messages may depend on private data. A secure stack uses data-independent padding where required, canonical compilation, fixed transcript formats, authenticated session identifiers, and coarse abort categories. Diagnostic logs must not reveal secret masks or private feed-forward data.
Collusion and endpoint compromise
Section titled “Collusion and endpoint compromise”Multi-client and multi-server claims must list allowed coalitions. A protocol secure against one malicious server may fail if that server colludes with a client, source, orchestrator, or second server. Blindness also does not protect against malware that reads Alice’s input before encryption or her output after decryption.
Choosing the client’s assumptions
Section titled “Choosing the client’s assumptions”A client that can prepare a small set of calibrated states can use prepare-and-send UBQC. A measurement client reverses the quantum link and must account for malicious incoming light and the protocol’s detector assumptions. A fully classical client in the constructions discussed here uses either separated provers or computational assumptions. These choices exchange physical and cryptographic requirements; they do not form a simple hierarchy.
Blindness, accepted-output accuracy and honest acceptance must all match the implemented interface. A universal gate set or a small trap demonstration alone does not establish a large verified computation. The distributed-computing page treats remote gates and network scheduling; the privacy guarantees here additionally depend on what each server is allowed to learn.
Exercises
Section titled “Exercises”1: Separate the guarantees
Section titled “1: Separate the guarantees”A protocol encrypts Alice’s input perfectly, but Bob may replace the output with any string and Alice always accepts. Classify its correctness, blindness, verifiability, and availability against malicious Bob.
Solution
The encryption may provide perfect blindness for the input, provided the full view and leakage are covered by a proof. The protocol is not verifiable because Bob can make Alice accept a wrong result with probability one. Its honest correctness may still be perfect if an honest Bob computes correctly. It has no malicious-server availability guarantee because Bob can return nonsense or stop. The four statements concern different experiments.
2: Average the phase ensemble
Section titled “2: Average the phase ensemble”Show directly that uniformly averaging over for gives .
Solution
Write
The diagonal entries average to . The off-diagonal sum is a geometric series over all eighth roots of unity:
The conjugate sum also vanishes, leaving .
3: Decode a masked instruction
Section titled “3: Decode a masked instruction”Let , , , , and . Compute and the angle sent to Bob. If Bob returns , what outcome does Alice record?
Solution
The corrected angle is
Therefore
Alice decodes .
4: Leakage and padding
Section titled “4: Leakage and padding”Two private circuits compile to brickwork graphs of dimensions and . Alice pads both to . What circuit information is hidden, and what still leaks if message timing follows graph layers?
Solution
Bob can no longer distinguish the two circuits from the graph dimensions; he learns only that the compiled computation fits inside , assuming the dummy construction is itself blind. If timing reveals which layers contain real adaptive work, the active depth or dependency pattern may still leak. Alice needs a fixed schedule and fixed transcript shape if those properties are intended to be hidden. Network identity, total padded size, and the fact that a session occurred remain visible unless separately protected.
5: Toy trap amplification
Section titled “5: Toy trap amplification”In a simplified independent-round model, any fixed corrupting attack triggers a trap with probability at least per repetition. How many repetitions make the miss probability at most ?
Solution
We need
Thus
Since is an integer and direct substitution is required, is the first value strictly below . A real protocol needs a proof against coherent attacks and cannot assume independent detection events without justification.
6: Pauli-key update through a Hadamard gate
Section titled “6: Pauli-key update through a Hadamard gate”An encrypted qubit is . Show that after Bob applies , Alice can regard the output as an encryption of with updated key , up to an irrelevant global phase.
Solution
Using and ,
The factor is a global phase. Therefore the new key is and the new key is . Clifford gates permit this efficient classical key tracking; non-Clifford gates require additional machinery.
7: Choose a client model
Section titled “7: Choose a client model”Alice has no qubit source but has a well-characterized single-photon detector. She requires information-theoretic blindness from one server and can receive photons over a quantum link. Which family is the natural starting point, and which assumptions still need examination?
Solution
A receive-and-measure or remote-state-preparation protocol is the natural starting point. Alice must still state whether her measurement device is trusted or covered by the protocol proof, constrain incoming optical modes and intensity, handle loss without selective-reporting leakage, protect basis and outcome data inside her laboratory, authenticate classical communication, and verify that the server-memory and heralding model matches the theorem. Having a detector does not by itself establish device independence.
8: Remove the outcome pad
Section titled “8: Remove the outcome pad”Consider the single-round construction with , uniform and target . Bob receives and modulo . Show that both marginals are independent of , but Bob can recover exactly from their joint state.
Solution
The qubit average is and is uniform on eight angles for either target. After receiving , Bob measures in the basis . If , the sent state is ; if , it is . The outcome identifies the target with probability one. Separate privacy of each marginal does not imply privacy of their correlations. Restoring a secret uniform mixes these two orthogonal states for either target and removes this attack.
References
Section titled “References”- D. Aharonov, M. Ben-Or, E. Eban, and U. Mahadev, “Interactive proofs for quantum computations,” SIAM Journal on Computing 46, 1230–1272 (2017), arXiv:1704.04487.
- A. Broadbent, J. Fitzsimons, and E. Kashefi, “Universal blind quantum computation,” in 50th Annual IEEE Symposium on Foundations of Computer Science, 517–526 (2009), doi:10.1109/FOCS.2009.36.
- A. Broadbent and S. Jeffery, “Quantum homomorphic encryption for circuits of low -gate complexity,” in Advances in Cryptology – CRYPTO 2015, 609–629 (2015), arXiv:1412.8766.
- V. Dunjko, J. F. Fitzsimons, C. Portmann, and R. Renner, “Composable security of delegated quantum computation,” in Advances in Cryptology – ASIACRYPT 2014, 406–425 (2014), doi:10.1007/978-3-662-45608-8_22.
- J. F. Fitzsimons and E. Kashefi, “Unconditionally verifiable blind quantum computation,” Physical Review A 96, 012303 (2017), doi:10.1103/PhysRevA.96.012303.
- U. Mahadev, “Classical verification of quantum computations,” in 59th Annual IEEE Symposium on Foundations of Computer Science, 259–267 (2018), doi:10.1109/FOCS.2018.00033.
- T. Morimae and K. Fujii, “Blind quantum computation protocol in which Alice only makes measurements,” Physical Review A 87, 050301(R) (2013), doi:10.1103/PhysRevA.87.050301.
- B. W. Reichardt, F. Unger, and U. Vazirani, “Classical command of quantum systems,” Nature 496, 456–460 (2013), doi:10.1038/nature12035.
- L. Yu, C. A. Pérez-Delgado, and J. F. Fitzsimons, “Limitations on information-theoretically secure quantum homomorphic encryption,” Physical Review A 90, 050303(R) (2014), doi:10.1103/PhysRevA.90.050303.