

Decoy-State QKD
Decoy-state quantum key distribution is a parameter-estimation method for QKD transmitters that emit phase-randomized weak coherent pulses rather than deterministic single photons. Alice randomly changes the pulse intensity. The different intensity classes contain different known mixtures of vacuum, one-photon, and multiphoton emissions, yet a pulse containing exactly photons is required to have the same relevant quantum state regardless of the intensity label. Comparing the observed detection and error rates then bounds the yield and error rate of the one-photon sector.
This page derives the vacuum-plus-weak-decoy bounds, first for exact probabilities and then with the qualifications needed for finite data. Decoy estimation supplies one ingredient of a security proof; source characterization, authentication and the remaining classical processing are still required.
Required background. QKD explains secrecy and classical processing; BB84 distinguishes bit and phase errors. Photon-number states explains the optical number basis.
Weak laser pulses and photon-number splitting
Section titled “Weak laser pulses and photon-number splitting”Weak laser pulses are not single photons
Section titled “Weak laser pulses are not single photons”An attenuated laser pulse is naturally modeled as a coherent state. Here means photons in the same encoded optical mode; the fixed BB84 state label is suppressed. If its mean photon number is , write its complex amplitude as . In the photon-number basis,
If Alice uniformly randomizes the global optical phase independently on every pulse and does not reveal it, averaging over removes the coherence between distinct photon-number sectors:
The pulse is therefore a classical Poisson mixture of photon-number states, not a coherent superposition between sectors for the security model being used. In particular,
Vacuum pulses do not normally carry Alice’s bit. One-photon pulses support the qubit security argument. Multiphoton pulses require special care because two or more copies of the same encoded optical state may leave the transmitter.
The photon-number-splitting warning
Section titled “The photon-number-splitting warning”Consider a highly lossy channel and suppose Alice and Bob inspect only the overall click probability and quantum bit error rate. An adversary can, as an illustrative attack, perform a quantum-nondemolition measurement of photon number, block selected vacuum and one-photon pulses, and remove one photon from a multiphoton pulse while forwarding the rest losslessly. Eve stores her photon until Alice announces the basis and then measures in that basis. On those forwarded multiphoton rounds she can learn the bit without introducing the intercept–resend error signature.
The point is not that every real attack literally uses a photon-number splitter. The point is non-identifiability. One overall detection rate can be explained by many different photon-number-dependent channel responses. A low observed error rate does not by itself show that enough detections came from the one-photon sector.
In the conservative tagged-signal treatment of Gottesman et al. (2004), every multiphoton emission is treated as known to Eve, the key-producing resource is the number of detected one-photon signals. Without additional observations, Alice and Bob cannot estimate that number tightly in a high-loss channel. Decoy intensities supply those observations.
The Decoy-State Principle
Section titled “The Decoy-State Principle”Alice chooses an intensity label at random for each pulse. A common three-intensity design uses
where is the signal intensity, is a weak decoy intensity, and is a vacuum decoy. The intensity label is normally disclosed over the authenticated public channel only after Bob has fixed his detection record.
The key assumption is that, for a fixed photon number and encoded BB84 state, signal and decoy emissions have identical conditional states in all modes accessible to Eve. Changing the intensity changes the probabilities of the photon-number sectors, not their conditional polarization, timing, spectrum or spatial profile. This is the principle behind the proposals of Hwang (2003), Lo, Ma and Chen (2005), and Wang (2005).
Knowing can change Eve’s posterior probability of the intensity label: large photon numbers are more likely for the brighter setting. The assumption does not forbid that ordinary statistical information. It says that at fixed there is no additional distinguishable label carried by the state. Before the intensity announcement, Eve therefore applies the same conditional response to identical -photon inputs. A source with intensity-dependent timing or spectrum needs a different analysis.
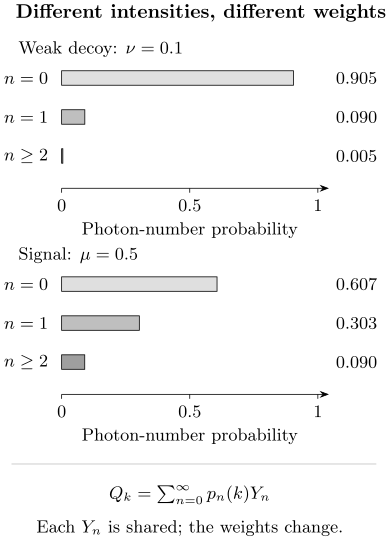
The brighter setting gives more weight to the one-photon and multiphoton sectors. Each individual -photon yield is shared between settings under the stated source assumptions. The grouped bar illustrates source composition only: its conditional mean yield need not be the same at the two intensities, because the mixture within that group changes.
Yields, Gains, and Error Gains
Section titled “Yields, Gains, and Error Gains”Suppress the basis label temporarily. For an emitted -photon pulse, define the yield
Define the conditional error rate
For intensity , the experimentally accessible gain and error gain are
where is the observed QBER among detected rounds of that intensity. In the stationary asymptotic model, the Poisson mixture and conditional-indistinguishability assumption give
It is useful to remove the common Poisson factor:
These are exponential generating functions for the yields and error yields. With an ideal continuum of exactly known intensities near zero,
This infinite-decoy limit gives the clean intuition. A practical experiment uses only a few intensities and finite counts, so it obtains bounds rather than an exact inversion.
The same definitions are applied separately by basis in a modern proof. For example, and the number of detected single-photon -basis signals enter the key length, while -basis data help bound the corresponding phase error. Writing one basis-independent is an expository simplification, not permission to average incompatible data sets.
Vacuum-Plus-Weak Bounds
Section titled “Vacuum-Plus-Weak Bounds”The three settings already give a useful analytic estimate. For a true vacuum decoy,
If Alice’s vacuum-round bit is uniform, private and independent of the detector output and acceptance, then . Bob’s background output need not itself be unbiased: comparing any independent bit with Alice’s uniform bit gives disagreement one-half. Bit leakage or bit-dependent acceptance can invalidate this argument. Vacuum data estimate the background yield and error gain under the actual assignment rules.
Lower bound on the one-photon yield
Section titled “Lower bound on the one-photon yield”Expand the weak and signal gains:
Form the combination
Because and , every term in the last line is nonpositive. The coefficient vanishes, and the coefficients for are negative. Therefore
Solving for gives the vacuum-plus-weak lower bound of Ma et al. (2005)
A negative right-hand side may be replaced by zero, using . In contrast, a lower bound above one signals inconsistent data or assumptions; replacing it by one does not repair the inference. Exercise 3 gives a simple example. Below, denotes the nonnegative bound from a consistent model.
With valid simultaneous confidence intervals for this model, the adverse substitutions use a lower bound for and upper bounds for and . Point estimates are not exact probabilities, and a finite-key proof must justify both those intervals and their conversion to photon-number counts.
The single-photon contribution to signal-intensity detections is then bounded by
Upper bound on the one-photon error rate
Section titled “Upper bound on the one-photon error rate”All error-yield terms are nonnegative, so the weak-decoy error gain satisfies
Consequently,
This requires . If it is zero, the data have not certified a positive one-photon contribution, and division by zero supplies no error estimate. In a consistent exact-probability model the numerator is nonnegative. A negative value is another consistency failure; with finite data, one must use a jointly valid confidence region rather than independently repair unfavorable estimates.
The numerator is made large and the denominator small for a conservative bound: use an upper bound on the weak-decoy error gain and a lower bound on the background error yield. An error probability can be capped at one. Capping its upper bound at one-half is different and generally invalid. If all that is known is , then the worst binary entropy is
For , the allowed interval includes the maximally uncertain value , so this entropy bound leaves no positive one-photon privacy term. It does not imply that the actual error is at most one-half.
With more intensities, numerical optimization can improve the bounds. Writing makes the gain constraints linear in . Minimizing and maximizing separately gives a conservative ratio when the denominator is positive. Optimizing the ratio itself is a linear-fractional problem, not simply a linear objective.
Worked Channel Example
Section titled “Worked Channel Example”Take an illustrative threshold-detector model with overall one-photon transmission-and-detection efficiency , background yield , background error probability , and optical misalignment error . A simple low-background model is
The second expression neglects the small overlap between a background event and a signal-origin event; it is a calculation model, not a detector security proof. Choose
The predicted signal and decoy observations are
Substitution in the analytic bounds gives
and hence
For comparison, the channel model’s actual one-photon yield is
The bound is lower, as it must be, but remains close enough to certify a substantial single-photon contribution. Without intensity variation, the same overall signal gain would not determine that contribution.
From a Yield Bound to a Key Rate
Section titled “From a Yield Bound to a Key Rate”In BB84 the privacy term uses a one-photon phase-error bound. Conjugate-basis decoy data can supply it under the source and sampling assumptions of the security proof. An aggregate signal QBER cannot be substituted for it. In the symmetric example here, the bound also bounds the phase error; write for the entropy maximizer just discussed.
The asymptotic tagged-signal treatment counts multiphoton detections as fully compromised. Omitting any possible positive vacuum contribution gives the achievable rate bound (Lo, Ma and Chen, 2005; Ma et al., 2005)
where
is the binary entropy, describes reconciliation inefficiency, and is a declared signal-and-basis selection prefactor. In the traditional symmetric BB84 convention with an asymptotically negligible decoy fraction, . If signal intensity is chosen with probability and only - rounds make key, then a rate per emitted pulse instead contains the corresponding factor .
For the numerical example, taking gives the bracketed quantity
Thus the conventional example yields approximately secret bits per emitted pulse before finite-key, authentication, and other implementation overheads. A positive asymptotic number is not a claim about a finite device run.
Finite-Key Estimation
Section titled “Finite-Key Estimation”A real block supplies counts, not exact probabilities. For each intensity and basis class , let count the pulses sent, count accepted detections, and count wrong detected bits.
The observed ratios are
Finite-key analysis needs simultaneous bounds with a stated joint failure probability. For a stationary shared-yield model, confidence intervals on the expected gains lead to constraints such as
These constraints illustrate the optimization. Under general correlated attacks, empirical yields from distinct samples need not coincide exactly. A security proof must justify the appropriate statistical comparison and convert it into bounds on actual one-photon counts and phase errors. Applying binomial intervals to observed gains and solving this stationary model is not by itself such a proof.
Subject to and , one can bound the single-photon yield and error yield as above. A numerical linear program truncates the photon number at and accounts for the known Poisson tail
Since , the omitted gain is between zero and . Thus a conservative truncated constraint is
Error tails also lie between zero and the corresponding gain tails. Retaining their joint constraints can tighten the result. Setting the tail to zero without a bound can exclude physically allowed explanations of the data.
A conservative finite-key expression, omitting a possible positive vacuum term, has the structure
where bounds detected one-photon key-basis events, bounds their phase-error rate, is the actual reconciliation leakage, and represents the proof’s verification and hashing length deductions. Statistical failures and smoothing parameters also enter the total correctness and secrecy error; they are not universally interchangeable fixed bit penalties. Lim et al. (2014) give a composable construction against general attacks with explicit constants, statistical bounds and a vacuum contribution, under specified source and receiver assumptions including basis-independent detection probability. The QKD overview explains the underlying entropy-to-key step.
Why more decoys can still mean less key
Section titled “Why more decoys can still mean less key”Additional intensity settings add constraints, but finite samples must be divided among more classes. A very weak decoy is informative about only if it produces enough detections to control fluctuations. A vacuum setting measures background directly but produces few useful events by design. The signal intensity, decoy intensities, basis biases, and selection probabilities therefore need joint optimization for the expected channel, block duration, detector behavior, and security target.
Rules of thumb such as and are useful starting points for some fiber links, not protocol constants. At long distance, the best allocation may devote a substantial fraction of pulses to parameter estimation. In a changing channel, an optimization based on a favorable past block can also bias the analysis unless adaptation is specified in advance or covered by the proof.
Source assumptions and finite data
Section titled “Source assumptions and finite data”Phase randomization
Section titled “Phase randomization”The Poisson mixture follows from averaging a uniformly random global phase. Attenuation alone does not perform that average. Gain-switching a laser may produce substantial phase randomization under characterized operating conditions, but it is not a mathematical guarantee for every pulse. Residual phase coherence can let Eve distinguish or coherently combine states in ways excluded by the photon-number-channel model. A transmitter should actively randomize or otherwise validate the phase model used by its proof.
Lo and Preskill (2007) analyze security with nonrandom phases under their specified source assumptions. The state decomposition and proof differ from the phase-randomized case. The standard decoy equations must not be imported unchanged.
Intensity calibration and fluctuations
Section titled “Intensity calibration and fluctuations”The symbols and represent physical photon-number distributions, not merely digital control values. Modulator calibration, laser power drift, finite extinction, pulse-shape changes, and monitor uncertainty produce intervals or correlations in the actual intensities. A sound analysis either bounds the emitted distribution pulse by pulse or uses a security proof that explicitly tolerates the characterized fluctuation model.
Replacing an uncertain by its nominal value can move Poisson weights in the favorable direction and overestimate . The conservative endpoint is not always the same for every coefficient, so blindly inserting one worst intensity into every term is not generally valid.
No intensity side channel at fixed photon number
Section titled “No intensity side channel at fixed photon number”Signal and decoy pulses can differ in spectrum, timing, chirp, spatial mode, polarization, pulse duration, or back-reflected light. If Eve can infer the intensity class before acting on the pulse, the correct variables are rather than shared . The standard system then loses its cross-intensity constraint.
This issue is especially important when separate lasers generate signal and decoy pulses. A single laser followed by a characterized intensity modulator can reduce some differences, but the modulator itself can introduce chirp or pattern dependence. Optical isolation, filtering, watchdog monitoring, and Trojan-horse bounds address parts of the engineering problem; their residual assumptions still belong in the security statement.
Correlations and detector behavior
Section titled “Correlations and detector behavior”Dead time, afterpulsing, modulator memory, feedback control, and thermal drift can correlate neighboring rounds. A proof based on independent and identically distributed trials is not automatically valid for such a source or receiver. Modern analyses may use martingale, entropy-accumulation, or explicit source-memory methods, but the observed data must match the chosen model.
Decoy states do not remove detector side channels. Detector blinding, efficiency mismatch, time-shift attacks, and mode-dependent acceptance remain receiver-model questions. Measurement-Device-Independent QKD combines two-source decoy estimation with an untrusted measurement station to move that particular trust boundary; it still relies on source characterization and decoy-state assumptions.
A signal plus one nonzero decoy removes the dedicated vacuum setting, but then the background contribution must be bounded indirectly. Rusca et al. (2018) analyze such a one-decoy protocol in finite blocks. The vacuum-plus-weak formulas cannot simply be reused with an unknown . More elaborate basis-dependent or passive choices likewise require the corresponding conditional source model and statistical analysis.
Exercises
Section titled “Exercises”1. Phase averaging
Section titled “1. Phase averaging”Starting from the coherent-state expansion, prove that uniform phase randomization produces a diagonal Poisson mixture.
Solution
Expand the projector:
Uniform averaging uses
Only remains, giving
2. Multiphoton probability
Section titled “2. Multiphoton probability”Show that . Find its leading behavior for and evaluate it at .
Solution
Subtract the vacuum and one-photon probabilities from unity:
Using gives
At ,
Thus roughly nine percent of emitted signal pulses are multiphoton in this source model, even though loss makes the detected fraction quite different.
3. An impossible yield estimate
Section titled “3. An impossible yield estimate”Suppose exact gains are reported as , , and for , . Evaluate the analytic lower bound. Can clipping it to one give a valid estimate?
Solution
The formula gives
This contradicts . More directly, every Poisson weight at is positive. Since all yields are nonnegative, forces every , which also forces . There is no shared-yield model for the stated exact data. Clipping the answer would conceal that inconsistency. Finite counts instead require a justified confidence region, which may contain consistent probabilities even when their point estimates do not.
4. Derive the error bound
Section titled “4. Derive the error bound”Starting from , derive an upper bound on when . Explain why replacing by a lower bound is conservative. If the resulting upper bound is , what entropy bound may be used?
Solution
Nonnegative multiphoton error yields imply
Therefore
For a nonnegative numerator and positive denominator, decreasing the denominator increases the ratio. Thus preserves the upper bound. A finite analysis uses simultaneous adverse bounds on all quantities.
If the result is , the allowed interval contains , where . Hence the safe entropy bound is one, not . The latter would overstate the private fraction. Nor may one conclude that the actual error is at most one-half.
5. Reproduce the channel estimate
Section titled “5. Reproduce the channel estimate”Use the worked-example parameters to calculate , , and . Compare the yield bound with the model value .
Solution
The gains and error rates are
Substitution gives
and
The model value is , so the analytic lower bound is about of the actual value in this asymptotic calculation without sampling fluctuations.
6. Infinite-decoy reconstruction
Section titled “6. Infinite-decoy reconstruction”Suppose is known exactly for all in a neighborhood of zero. Show how to reconstruct , , and .
Solution
Define . Its series is
Hence
In general . Exact differentiation is only an intuition for the infinite-data, continuous-intensity limit; numerical differentiation of noisy experimental gains would be unstable.
7. A distinguishable-decoy failure
Section titled “7. A distinguishable-decoy failure”Suppose weak-decoy pulses are delayed by relative to signal pulses, and Eve can resolve that delay before deciding whether to forward a pulse. Identify the failed equation and explain what source information or analysis is needed.
Solution
At fixed photon number, Eve can infer the class from arrival time. The shared yield model fails: one must allow
Then comparing and no longer constrains one common . Alice needs source characterization showing that the delay is absent or bounded strongly enough for a proof with distinguishable states, or she needs a protocol and security analysis that explicitly includes the leaked timing information. Relabeling the pulses does not repair the model.
8. Finite-key resource allocation
Section titled “8. Finite-key resource allocation”Alice can reduce the weak-decoy probability to send more signal pulses. Give one benefit and two costs of doing so in a fixed-duration experiment.
Solution
The benefit is a larger expected number of signal-and-key-basis detections, which can increase the raw material for the final key. The costs are fewer weak-decoy detections and therefore wider confidence intervals for and . A looser lower bound on or a looser upper bound on the phase error can erase the gain or force abort. The best probability is therefore a finite-block optimization, not “as few decoys as possible.” Channel drift can add a third cost if the smaller sample no longer diagnoses nonstationarity.
References
Section titled “References”- D. Gottesman, H.-K. Lo, N. Lütkenhaus, and J. Preskill, “Security of Quantum Key Distribution with Imperfect Devices,” Quantum Information and Computation 4, 325–360 (2004), doi:10.26421/QIC4.5-1.
- W.-Y. Hwang, “Quantum Key Distribution with High Loss: Toward Global Secure Communication,” Physical Review Letters 91, 057901 (2003), doi:10.1103/PhysRevLett.91.057901.
- C. C. W. Lim, M. Curty, N. Walenta, F. Xu, and H. Zbinden, “Concise Security Bounds for Practical Decoy-State Quantum Key Distribution,” Physical Review A 89, 022307 (2014), doi:10.1103/PhysRevA.89.022307.
- H.-K. Lo, X. Ma, and K. Chen, “Decoy State Quantum Key Distribution,” Physical Review Letters 94, 230504 (2005), doi:10.1103/PhysRevLett.94.230504.
- H.-K. Lo and J. Preskill, “Security of Quantum Key Distribution Using Weak Coherent States with Nonrandom Phases,” Quantum Information and Computation 7, 431–458 (2007), doi:10.26421/QIC7.5-6-2.
- X. Ma, B. Qi, Y. Zhao, and H.-K. Lo, “Practical Decoy State for Quantum Key Distribution,” Physical Review A 72, 012326 (2005), doi:10.1103/PhysRevA.72.012326.
- D. Rusca, A. Boaron, F. Grünenfelder, A. Martin, and H. Zbinden, “Finite-Key Analysis for the 1-Decoy State QKD Protocol,” Applied Physics Letters 112, 171104 (2018), doi:10.1063/1.5023340.
- X.-B. Wang, “Beating the Photon-Number-Splitting Attack in Practical Quantum Cryptography,” Physical Review Letters 94, 230503 (2005), doi:10.1103/PhysRevLett.94.230503.