

Device-Independent QKD
Device-independent quantum key distribution (DIQKD) is QKD whose secrecy proof treats the quantum source and endpoint measurement devices through their observed classical input-output behavior rather than through a trusted model of their Hilbert-space dimension, states, observables, efficiencies, or internal implementation. Alice and Bob repeatedly choose private inputs and , record outputs and , and test whether the conditional frequencies violate a Bell inequality. A loophole-aware violation can then lower-bound an adversary’s uncertainty about designated key outcomes.
The adjective device-independent does not mean assumption-free. The result still depends on quantum mechanics, authenticated classical communication, private and sufficiently independent input randomness, secure laboratories, trusted classical postprocessing, a causal trial definition, and a rule that prevents the two measurement boxes from exchanging their current inputs or outputs during a trial. Losses and no-clicks must be included without an unjustified fair-sampling assumption. An adversary may always make the protocol abort.
This page explains a CHSH-based protocol, its entropy bound and the assumptions needed to turn finite data into a key. The experimental apparatus can be complicated; the mathematical question is whether every quantum realization compatible with the observations leaves enough uncertainty for Eve.
Required background. QKD supplies the secrecy definition and classical processing. E91 introduces entanglement-based keys, the CHSH inequality supplies the local and quantum bounds, and entanglement certification distinguishes device-dependent witnesses from Bell tests.
Quantum devices through classical inputs and outputs
Section titled “Quantum devices through classical inputs and outputs”In a representative bipartite protocol, Alice’s box accepts an input and returns ; Bob’s box accepts and returns . The observed object is
The security proof does not need Alice and Bob to assert that the boxes contain qubits, Pauli measurements, polarizers, ion readout, or any fixed-dimensional system. A compatible quantum realization may instead use an unknown state and unknown measurement operators,
where neither the dimension nor the operators need be known to the users. Eve may have prepared the source, built the boxes, and retained the purifying system .
This freedom is constrained at the interface. Alice and Bob must know which input they supplied, receive one declared output for every eligible trial, and prevent unauthorized information from leaving their laboratories. During a trial, Alice’s current input and output cannot reach Bob’s box, and conversely. The boxes may retain memory of earlier trials unless the proof explicitly assumes otherwise, so security against a general sequential attack must allow the th response to depend on the entire permitted past.
The trusted parts are the private input choices, laboratory isolation, the timing and output rules, authenticated communication, and classical processing. The source and measurement internals may be adversarial. Efficiency need not be calibrated for the secrecy proof, but missing detections must appear in the prescribed statistics.
A CHSH-based key protocol
Section titled “A CHSH-based key protocol”Many DIQKD proofs use variants rather than one universal protocol. The following skeleton isolates the common logic.
- Fix the protocol. Alice and Bob authenticate their public channel, allocate private random seeds, fix a trial clock and outcome alphabet, and commit to all acceptance thresholds before collecting data.
- Define an eligible trial. In a direct experiment every clocked attempt may count. In an event-ready architecture, a flag announces that entanglement distribution succeeded. Crucially, is fixed before the private inputs are generated.
- Choose the inputs. Trusted local controllers implement the prescribed joint distribution of test and generation inputs. A private selector may coordinate this choice. It is not an extra input handed to the untrusted boxes: each box receives only its local measurement setting, and any information that setting reveals is included in the proof.
- Query the boxes. Alice supplies , Bob supplies , and each box must return exactly one output under the protocol’s alphabet and timeout rule. A no-click is an outcome or is deterministically mapped to one; it is not silently erased.
- Fix the transcript. The outputs are committed before settings, round types, or test outcomes are disclosed. This ordering prevents the boxes from tailoring outputs to later public information.
- Estimate behavior. Alice and Bob reveal test data, calculate the Bell score, estimate the key-basis error rate, and abort unless both lie in the proved acceptance region.
- Distill the key. They reconcile the retained raw strings, verify agreement, and apply privacy amplification at a length justified by the entropy bound and every disclosed bit.
A common CHSH layout gives Alice two test inputs and Bob two test inputs . Bob has an additional setting aligned with Alice’s setting for key generation. Other protocols use two key bases, biased inputs, asymmetric Bell inequalities, or full-distribution estimators. Those changes alter the rate and finite-size proof, not the basic need to connect test behavior to the actual key output.
In this layout, Alice’s outcome is the raw-key variable. Bob’s extra setting makes his outcome agree with it; Alice sends reconciliation information to Bob. The same Alice input occurs in both test and generation rounds. Revealing an additional round-type flag to her box could let it behave honestly only during tests, as exercise 4 demonstrates.
The Bell-Test Statistic
Section titled “The Bell-Test Statistic”Map binary outputs to signs,
and define the test-round correlators
With one standard sign convention, the CHSH expression is
Bell-local correlations obey , while quantum theory allows . Equivalently, Alice and Bob win the CHSH game when . For uniformly distributed test inputs,
after choosing output labels so that . The local and quantum limits are
The full conditional distribution can give tighter entropy estimates than one scalar score. Brown, Fawzi and Fawzi (2021), for example, develop numerical entropy bounds for quantum correlations. Here CHSH gives a tractable analytic example.
Why Nonlocality Can Imply Privacy
Section titled “Why Nonlocality Can Imply Privacy”A Bell violation rules out a shared deterministic instruction list that explains the accepted data while respecting the trial’s causal constraints. Quantum nonlocality also obeys monogamy: correlations that are close to the maximal bipartite CHSH value cannot be simultaneously shared with Eve in a way that lets her predict the key output perfectly. A security proof makes this intuition quantitative by minimizing an entropy over every quantum realization compatible with the data.
For a classical key symbol and quantum side information , conditional min-entropy has the operational meaning
where is Eve’s optimal probability of identifying . Privacy amplification converts a string with sufficiently large smooth conditional min-entropy into a shorter string close to uniform and independent of Eve. A Bell score is useful because it supplies a device-independent lower bound on that entropy.
A Bell violation alone is not yet a key. Alice and Bob also need correlated generation outcomes, enough finite data to exclude a weaker underlying score, an analysis valid against the allowed temporal correlations, an accounting of the public reconciliation transcript, and a composable extractor statement.
Representative Asymptotic CHSH Rate
Section titled “Representative Asymptotic CHSH Rate”The calculation of Acín et al. (2007) and Pironio et al. (2009) assumes asymptotically many rounds, binary outputs, one-way reconciliation and collective attacks. We exchange the original papers’ party labels so that the protected key output is Alice’s , which participates in CHSH. Bob’s extra key setting is used only to improve agreement. Let be their key disagreement probability after the declared relabeling.
For the Holevo-information form below, symmetrize each pair of outputs by an independent shared random flip : , . The flip is public and belongs in Eve’s side information. It makes the marginal output uniform while preserving all correlators and ; it does not hide anything from Eve. Write for the symmetrized Alice key bit. With , the bound is
Equivalently, . We use the positive CHSH convention . Equivalent sign conventions give the corresponding bound in .
Combining this with the reconciliation cost gives the achievable secret fraction
At the local boundary, . At maximal CHSH violation, . Between them the available private entropy must still exceed the reconciliation cost.
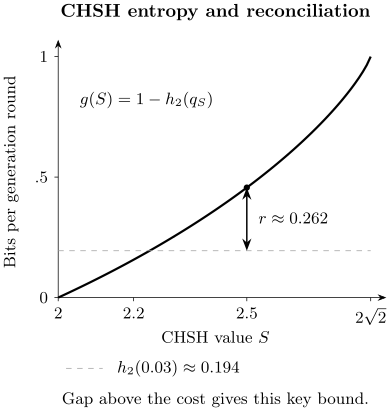
The solid curve is the collective-attack entropy bound . At key error , the dashed line is the ideal reconciliation cost . The vertical gap at is about secret bits per generation round. A violation just above two does not yet make this rate bound positive. Finite-data deductions lower the achievable fraction further.
This formula is a useful diagnostic, not a universal DIQKD theorem. It is per retained generation round under its specified asymptotic model. It omits test allocation, imperfect reconciliation, finite-statistical margins, authentication consumption, heralding probability, source repetition rate, and protocol-dependent constant terms. General attacks require a sequential proof such as entropy accumulation.
A worked asymptotic fraction
Section titled “A worked asymptotic fraction”Suppose a representative experiment estimates
Then
and
The representative fraction is therefore
secret bits per retained key round. If reconciliation costs instead, the fraction becomes approximately . With a generation fraction and herald probability , this corresponds to about secret bits per optical attempt before finite-key deductions. Bits per retained round and bits per attempt are different quantities.
General Attacks and Entropy Accumulation
Section titled “General Attacks and Entropy Accumulation”An uncharacterized box may have memory. It can change strategy with time and correlate the current output with every earlier input, output, and public message it is allowed to know. Treating the data as independent and identically distributed merely because the histogram looks stationary is not a DI argument.
The entropy accumulation theorem (EAT; Dupuis, Fawzi and Renner, 2020) applies to sequential quantum processes satisfying its specified conditional-independence or Markov conditions. Fresh independent inputs, isolation and restrictions on leaked information are essential; chronological order alone is insufficient. Arnon-Friedman et al. (2018) show how to construct an appropriate DI cryptographic process. A protocol constructs a min-tradeoff function that lower-bounds the conditional von Neumann entropy produced by one admissible round as a function of its test statistics. Conditioned on passing the parameter-estimation test, a schematic EAT statement has the form
where:
- is the number of protocol rounds; includes their test/generation allocation and the specified key map;
- is Alice’s raw key string;
- contains the settings, test disclosures, public symmetrization flips and other information already released before reconciliation;
- is the event that parameter estimation accepts;
- is a conservative Bell-test parameter or frequency region obtained from the observations and a one-sided statistical margin;
- contains finite-size terms, typically with leading behavior of order for a fixed protocol and error budget.
Neither nor is universal. They depend on the Bell game, input distribution, key map, output alphabet, acceptance event, entropy version, acceptance probability and proof technique. A bound for the normalized state conditioned on a rare acceptance event cannot be assumed independent of that event’s probability. A complete implementation should use the exact theorem and software corresponding to its protocol, including finite-precision rounding and failure allocation.
After parameter estimation, a representative key-length expression is
Here reconciliation leakage and the verification tag are subtracted only if they have not already been included in the conditioned transcript. The independent public extractor seed is included in the final secrecy statement, but its full length is not automatically a raw-key entropy loss. The QKD overview derives the hashing step and explains how smoothing, parameter-estimation and authentication errors compose.
Finite Data, Completeness, and Soundness
Section titled “Finite Data, Completeness, and Soundness”Completeness bounds abort probability for a specified honest implementation. It measures whether the protocol is useful under the expected noise and loss. Security bounds correctness failure and the operational distinguishability of the actual key from an ideal shared secret key, including the abort branch. Secrecy is a trace-distance statement, not generally a probability that a particular key is “nonsecret.” In a normalized accepted-state convention, its distance is weighted by the acceptance probability. An adversary’s ability to force abort violates neither definition.
For intuition only, suppose independent CHSH test rounds give empirical win fraction . Hoeffding’s (1963) inequality supplies the one-sided margin
At and ,
That reduction can materially change the entropy near threshold. For memory-bearing devices, one must state what is being bounded. For a fixed number of sequential test trials, let be the win indicator and . The conditional Hoeffding argument also gives
Thus the same numerical margin can lower-bound the average conditional winning probability even with memory. It does not establish one stationary underlying state or justify multiplying a one-round entropy by the key length. Sampling test versus key rounds, stopping rules and entropy accumulation still need the protocol’s sequential proof. Choosing a favorable stopping time is not covered by a fixed- bound.
Detection Loophole and No-Clicks
Section titled “Detection Loophole and No-Clicks”Suppose an adversarial box carries a local hidden variable and chooses whether to report a click as a function of its local input and . If Alice and Bob retain only double-click trials, the surviving subset can be highly nonrepresentative. The device can suppress outcomes that would reduce the desired correlation and make a Bell-local strategy look nonlocal. This is the detection loophole.
A valid DI treatment uses one of three proof-compatible approaches:
- retain no-click as an explicit output;
- map every no-click deterministically or randomly according to a committed rule and include the result in the Bell statistics;
- use an event-ready herald to define an eligible trial before the private settings are generated, then include every post-herald outcome.
Coincidence windows are part of the same issue. If a pairing rule is chosen after looking at detection times, or if setting-dependent timing changes which events are paired, postselection can open a loophole. Clock windows, timeout rules, double-click maps, and data exclusions must be fixed before the run.
Bell-test efficiency is not key-generating efficiency
Section titled “Bell-test efficiency is not key-generating efficiency”In an ideal symmetric CHSH experiment with maximally entangled states, no background, and the standard assignment of missed events, the familiar threshold for any Bell violation is
Eberhard (1993) showed that suitably chosen tests with nonmaximally entangled states can approach in an ideal low-background limit. Neither number is a universal DIQKD detector threshold. For a specified positive-error key model, crossing the Bell boundary need not provide enough entropy to pay reconciliation. Exercise 6 derives both thresholds in a simple independent-loss model; the resulting key threshold is about . It is a property of that model and rate bound, not a universal DIQKD efficiency requirement. Other states, inequalities, postprocessing and finite-key analyses give different values.
Event-Ready Heralding
Section titled “Event-Ready Heralding”An event-ready architecture separates channel loss from the Bell trial. A central station attempts entanglement generation or swapping and emits a flag . The valid causal order is
If , no Bell trial has begun. If , Alice and Bob choose fresh private inputs and every resulting output counts. The herald may depend on the adversarial source and its past, but not on future settings or post-herald outcomes. Channel loss before a valid herald reduces the event rate rather than allowing outcome-dependent selection. Detection failure after the herald still belongs to the output alphabet.
Matter qubits are attractive in this architecture because photons can herald remote entanglement while local atomic or ionic states are read out with high efficiency. Entanglement Swapping develops the conditional state update. DIQKD adds the stronger requirements that the heralding interface be causally ordered, the local measurements close the detection loophole, and the full transcript enter a key-security proof.
Locality, Input Independence, and Leakage
Section titled “Locality, Input Independence, and Leakage”Bell’s factorization assumption is only excluded when its causal premises match the experiment. Three interfaces deserve separate attention.
Communication during a trial
Section titled “Communication during a trial”If Bob’s box learns before choosing , the two boxes can reproduce any desired correlation by ordinary communication. Spacelike separation of input choice and remote output is the cleanest enforcement. Cryptographic DIQKD may instead assume shielded laboratories and timing controls that prevent cross-talk during the measurement interval. The latter is an explicit engineering assumption, not a conclusion derived from the Bell score.
Freedom of choice
Section titled “Freedom of choice”In the ideal model, the settings are sufficiently independent of Eve’s hidden information,
Perfect uniformity is not always necessary; specialized proofs can tolerate bounded bias or partial input leakage. But a device that predicts the settings well enough can prearrange favorable answers. The random generator, its seeding, timing, electronic fan-out, and electromagnetic leakage therefore remain inside the trusted boundary.
Laboratory leakage
Section titled “Laboratory leakage”An untrusted box can know old inputs and outputs. If it can modulate outgoing light, radio-frequency emission, timing, power draw, acoustic signals, or a later public output, it may exfiltrate raw key without contradicting the Bell statistics. Alice and Bob need secure laboratory boundaries or a quantitative leakage model. Device independence protects against an incorrect internal measurement model; it does not make an open side channel harmless.
Memory Across Trials and Sessions
Section titled “Memory Across Trials and Sessions”Within one run, entropy accumulation is designed to tolerate sequential memory: round may depend on all allowed earlier information. This is different from reusing a malicious device across protocol sessions. As Barrett, Colbeck and Kent (2013) explain, a box can store an earlier key and encode it into outcomes that will later be publicly revealed for parameter estimation. Such a memory attack can compromise composition even if each session’s within-run statistics look acceptable.
Countermeasures are protocol-specific. They can include isolating or securely retiring devices after a session, preventing a reused box from accessing old private registers, separating devices used with different counterparties, constraining future public communication, or using a composable architecture proved for reuse. “The EAT allows memory” does not by itself settle this cross-session leakage problem.
Secret bits per second
Section titled “Secret bits per second”The secret fraction is only one factor in throughput. For an event-ready system, a useful decomposition is
where is the entanglement-attempt rate, the valid herald probability, the fraction assigned to key generation and surviving protocol filters, and the finite-key secret fraction per retained generation outcome.
Direct photonic implementations can have a high attempt frequency but pay channel loss inside the Bell trial unless successful distribution is heralded. Matter memories can separate heralded optical distribution from efficient local readout, at the cost of waiting, decoherence and additional hardware. Multiplexing supplies parallel attempts but requires enough independent modes or memories.
If an architecture must wait for a herald across a total signaling path before reusing the same memory, its single-mode attempt rate is limited on the scale of , where is the speed of light in fiber. A simple round-trip path has , but the exact path is architecture-dependent. Multiplexing can launch many attempts before earlier heralds return, at the cost of more memories, modes, switching, and classical control.
Device-independent communication research discusses experimental and open-problem developments. When comparing results, distinguish positive asymptotic fractions from positive finite keys, and separate bits per herald, per optical attempt and per second. A Bell violation by itself supplies none of those key-rate conclusions.
MDI-QKD has a different premise: it trusts endpoint preparations while allowing an arbitrary central measurement. DIQKD instead constrains endpoint behavior through a Bell test within isolated laboratories. A Bell-state analyzer and a Bell-inequality test are different objects.
Exercises
Section titled “Exercises”1. Convert a CHSH win fraction
Section titled “1. Convert a CHSH win fraction”In uniformly sampled test rounds, Alice and Bob observe . Convert this to the corresponding point estimate . Does it violate the local bound?
Solution
Using ,
Because , the point estimate violates CHSH. A finite-data security claim must still replace this point estimate by a one-sided confidence bound and verify the other protocol conditions.
2. Evaluate the representative rate
Section titled “2. Evaluate the representative rate”Use the collective-attack asymptotic expression to calculate the secret fraction at and .
Solution
The Bell-dependent argument is
Numerically,
Therefore
This is per retained key round and inherits every assumption of the stated asymptotic collective-attack formula.
3. Apply a finite-sample margin
Section titled “3. Apply a finite-sample margin”For independent test rounds and , calculate the illustrative Hoeffding margin on and the resulting reduction in .
Solution
The one-sided margin is
Since , the Bell-score reduction is
Thus a point estimate becomes the illustrative lower bound . For sequential trials, the conditional-mean version in the text has the same numerical margin under its fixed-sample assumptions. Connecting it to entropy and to generation rounds still requires a valid sequential proof.
4. A leaked round-type flag
Section titled “4. A leaked round-type flag”Suppose Alice’s and Bob’s boxes receive an extra flag telling them whether a round is a test or key generation. During tests they use a maximally entangled pair and optimal CHSH measurements; during generation they both output zero. What are , and Eve’s key knowledge? Why is applying the displayed rate formula invalid?
Solution
The test data give , while the generation data have . Yet the raw key is a fixed string known to Eve. Even public simultaneous flips only turn it into a string of publicly known flip bits.
The calculation falsely identifies Alice’s tested observable with her generation observable. The hidden flag changes the device input: it is really . No Bell test constrained the key behavior. Withholding this extra flag, while including whatever the legitimate local setting reveals in the proof, is part of connecting test entropy to key outcomes.
5. Check a heralding timeline
Section titled “5. Check a heralding timeline”Consider two timelines:
Which one supports ordinary event-ready postselection, and why?
Solution
Timeline A supports event-ready postselection. The flag defines eligibility before either private setting exists, so channel failure cannot select a setting-dependent subset. In timeline B, the heralding device can know the settings and announce success only for favorable pairs. Treating rounds as nonexistent would then open a detection or selection loophole unless a specialized proof explicitly models that dependence.
6. Detection efficiency and a model key threshold
Section titled “6. Detection efficiency and a model key threshold”Take unbiased ideal CHSH correlations with and perfectly agreeing key outputs. Each endpoint detects independently with efficiency , independent of setting and ideal outcome. Map every no-click to bit zero. Derive and the key disagreement , then compare the Bell threshold with the zero of .
Solution
Double detections preserve the ideal correlations with weight . With exactly one detection, the unbiased detected sign averages to zero. Double misses give correlation , hence
Solving gives . In the key setting, double detections and double misses agree. Exactly one detection has probability and disagrees half the time, so
The positive-key crossing of the stated asymptotic bound is numerically . For example, at , Bell violation remains possible but this bound gives no key. This calculation assumes independent loss and a fixed output assignment; it is not a detector characterization used by a DI secrecy proof. It predicts honest-system performance under one chosen model.
7. Separate secrecy from availability
Section titled “7. Separate secrecy from availability”Eve blocks every entanglement attempt whenever Alice and Bob begin a DIQKD session. Has she violated the secrecy theorem?
Solution
No. Correctness and secrecy include the abort branch; with no accepted key there is no incorrect or leaked key output. The theorem does not promise successful distribution against blocking. This attack affects availability, while completeness describes abort probability under the specified honest implementation.
8. Identify a cross-session memory attack
Section titled “8. Identify a cross-session memory attack”A malicious box stores Alice’s first-session raw key. During a later session, it encodes those old bits into outputs selected for public parameter estimation. Why does within-run entropy accumulation not automatically stop this attack?
Solution
Entropy accumulation can permit temporal correlations while lower-bounding entropy for one causally ordered execution. It does not erase the box’s memory or forbid a later public transcript from carrying information about an earlier session. Composable reuse needs an additional device-reuse architecture, isolation of old private registers, constraints on later communication, or secure retirement of the device.
References
Section titled “References”- A. Acín, N. Brunner, N. Gisin, S. Massar, S. Pironio, and V. Scarani, “Device-independent security of quantum cryptography against collective attacks,” Physical Review Letters 98, 230501 (2007), doi:10.1103/PhysRevLett.98.230501.
- R. Arnon-Friedman, F. Dupuis, O. Fawzi, R. Renner, and T. Vidick, “Practical device-independent quantum cryptography via entropy accumulation,” Nature Communications 9, 459 (2018), doi:10.1038/s41467-017-02307-4.
- J. Barrett, R. Colbeck, and A. Kent, “Memory attacks on device-independent quantum cryptography,” Physical Review Letters 110, 010503 (2013), doi:10.1103/PhysRevLett.110.010503.
- P. Brown, H. Fawzi, and O. Fawzi, “Computing conditional entropies for quantum correlations,” Nature Communications 12, 575 (2021), doi:10.1038/s41467-020-20018-1.
- F. Dupuis, O. Fawzi, and R. Renner, “Entropy accumulation,” Communications in Mathematical Physics 379, 867–913 (2020), doi:10.1007/s00220-020-03839-5.
- P. H. Eberhard, “Background level and counter efficiencies required for a loophole-free Einstein–Podolsky–Rosen experiment,” Physical Review A 47, R747–R750 (1993), doi:10.1103/PhysRevA.47.R747.
- W. Hoeffding, “Probability Inequalities for Sums of Bounded Random Variables,” Journal of the American Statistical Association 58, 13–30 (1963), doi:10.1080/01621459.1963.10500830.
- S. Pironio, A. Acín, N. Brunner, N. Gisin, S. Massar, and V. Scarani, “Device-independent quantum key distribution secure against collective attacks,” New Journal of Physics 11, 045021 (2009), doi:10.1088/1367-2630/11/4/045021.