

Quantum Key Distribution
Quantum key distribution (QKD) is a family of interactive protocols through which two remote parties, conventionally Alice and Bob, generate matching secret classical bit strings. The security argument combines quantum measurements with authenticated classical postprocessing. The intended output is a key,
that is nearly uniform and nearly independent of everything available to an adversary Eve.
QKD is key establishment, not message transmission and not an encryption algorithm. Once generated, the key can be supplied to a one-time pad, an authenticated-encryption scheme, or another cryptographic application. The resulting application’s security depends on that later construction, its key management, its endpoints, and the way the QKD security guarantee composes with them.
The security question is quantitative: after all public discussion, how close is the resulting key to a uniform string unknown to Eve? Quantum signals help establish a bound on Eve’s information. Authentication, statistical estimation and classical processing turn that bound into a usable key.
Required background. No-cloning and no-signaling explain why quantum signals differ from copyable classical data. Density operators describe Eve’s quantum information, and entanglement measures distinguish shared entanglement from secret key. Helpful background. Classical information supplies entropy and reconciliation concepts; trace distance measures operational distinguishability.
Correctness, secrecy and abort
Section titled “Correctness, secrecy and abort”Systems and adversary
Section titled “Systems and adversary”Alice and Bob use:
- an insecure quantum channel, which Eve may control completely;
- a public but authenticated classical channel, which Eve may read but cannot modify or forge except with a bounded failure probability;
- local laboratories whose trusted components and leakage assumptions must be stated;
- local random choices with a specified quality and independence model.
A strong proof may allow Eve to replace the channel, inject arbitrary states, correlate all transmissions, retain a quantum memory indefinitely, postpone her measurement, and perform one joint coherent attack. This does not mean every implementation is secure against every physical attack. The proof only covers physical behavior represented by its model.
Let denote the event that the protocol passes all tests rather than aborting, let be the complete public transcript, and let denote Eve’s final quantum and classical side information. For simplicity, take a fixed output length whenever the protocol accepts. If the length varies with the transcript, the ideal key must have the corresponding length in each transcript branch. The distinctions below follow the composable formulation of Portmann and Renner (2014, 2022).
Correctness
Section titled “Correctness”The keys should disagree only with small probability:
An error-verification tag sent after reconciliation normally enforces this condition. A low observed quantum bit error rate alone does not guarantee identical final strings.
Secrecy
Section titled “Secrecy”For a nonzero acceptance probability , define the conditional distance
Here is the uniform classical key state. The ideal state has the same adversary information and transcript, but its key is independent of them. The composable secrecy condition is
The factor weights the accepted branch in the full protocol, which can also abort. It does not imply . The conditional conclusion is only , and can be weak for a very rare accepted run. Exercise 3 gives an exact one-bit example. When , no conditional key exists and this contribution to the full distance is zero.
Trace distance limits the change in probabilities of any subsequent test or use. It is not, without an additional interpretation, the literal probability that Eve has learned the entire key.
Composable soundness and honest abort
Section titled “Composable soundness and honest abort”Correctness and secrecy combine into an overall soundness error that can be bounded by
Composable security means the real key resource can replace an ideal key resource in a larger protocol while changing the larger system’s behavior by at most the declared error. Errors can be bounded by a sum when secure components are composed with compatible assumptions. If the QKD theorem assumes an ideal authenticated channel, an implementation with authentication error adds that error to the bound.
A separate robustness or completeness parameter controls honest abort:
Soundness limits the accepted-key discrepancy as part of the full protocol, including its probability of acceptance. Robustness asks whether an honest run is likely to produce one. Eve can always block the quantum channel and force an abort, so QKD does not guarantee availability or prevent denial of service.
End-to-End Protocol
Section titled “End-to-End Protocol”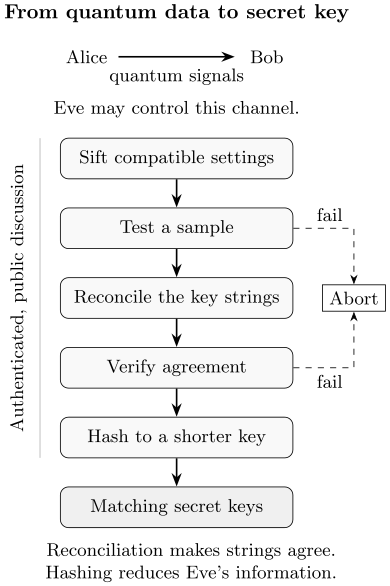
A generic QKD session. Eve may control the quantum channel and read the classical transcript. Authentication prevents undetected substitution of classical messages. Parameter estimation and verification can force an abort; privacy amplification converts a partially secret reconciled string into a shorter composably secret key.
The steps separate two problems. Reconciliation makes the parties’ strings agree; privacy amplification makes a shorter agreed string secret. Neither can replace the other.
| Step | What it establishes |
|---|---|
| Quantum exchange and sifting | Correlated data in compatible settings |
| Parameter estimation | A bound on errors or Eve’s information |
| Reconciliation | Bob’s estimate of Alice’s string |
| Verification | A bound on undetected disagreement |
| Privacy amplification | A shorter key close to uniform |
Classical messages are authenticated and visible to Eve. Settings, revealed samples, error-correction syndromes and verification tags therefore enter the security analysis. The proof must specify what remains secret after these disclosures.
Why Quantum Signals Help
Section titled “Why Quantum Signals Help”Prepare-and-measure protocols encode data in nonorthogonal quantum states. Entanglement-based protocols distribute correlations that cannot be reproduced under the protocol’s accepted parameter region without limiting Eve’s side information. In either description, incompatible measurements create a tradeoff: gaining predictive power about one key-generating observable constrains correlations in a complementary observable.
The security mechanism is therefore not simply “measurement disturbs the photon.” A modern proof connects observed statistics to a bound such as a conditional entropy,
or a smooth conditional min-entropy,
These quantify Eve’s uncertainty about Alice’s prospective key data under the declared model. Von Neumann Entropy supplies the asymptotic entropy language; smooth min-entropy is the one-shot quantity needed for finite blocks.
No-cloning is part of the physical background, but it does not quantify information gained by an approximate interaction, a multiphoton signal or a side channel. A security proof must connect actual measured statistics to Eve’s remaining information after public discussion.
Parameter estimation does not identify Eve or distinguish malicious disturbance from ordinary noise. It determines whether the observed data fall inside a region for which a security theorem certifies an acceptable key length.
Prepare-and-Measure Protocols
Section titled “Prepare-and-Measure Protocols”In a prepare-and-measure protocol, Alice chooses a classical symbol and setting, prepares a corresponding quantum state, and sends it to Bob. Bob chooses a measurement setting and records an outcome. Only later do they disclose enough setting information to sift and test the data.
BB84, introduced by Bennett and Brassard (1984), is the basic example: two conjugate qubit bases encode candidate key bits. The six-state protocol uses three mutually unbiased qubit bases and obtains more symmetric parameter information at the cost of additional setting choices. B92 uses two nonorthogonal states and an unambiguous-outcome structure. Continuous-variable protocols encode quadratures of optical modes and require a distinct detector, channel, and security analysis.
Real optical transmitters commonly emit phase-randomized weak coherent pulses rather than deterministic single photons. Such pulses contain vacuum, one-photon, and multiphoton components. Decoy-state methods vary the mean intensity so Alice and Bob can estimate the behavior of photon-number sectors and bound the single-photon contribution. Decoy analysis addresses photon-number-splitting vulnerabilities under its source assumptions; it does not certify every possible source imperfection.
The prepare-and-measure description is operationally direct, but security proofs often use a source-replacement picture. Alice may be imagined to prepare an entangled state
and measure to choose the signal sent through . This mathematical equivalence connects state preparation to entanglement and complementarity without requiring an actual entangled source in the laboratory.
Entanglement-Based Protocols
Section titled “Entanglement-Based Protocols”In an entanglement-based protocol, a source distributes bipartite systems and Alice and Bob choose local measurements. The source may be trusted, partially characterized, or entirely untrusted depending on the protocol. Some measurement outcomes form the raw key; others estimate correlations relevant to secrecy.
E91 uses entangled pairs and Bell-type correlations (Ekert, 1991). BBM92 gives an entanglement-based counterpart to BB84 (Bennett, Brassard and Mermin, 1992). Entanglement-based reasoning is especially useful because it turns secrecy into a statement about entanglement, complementarity, or monogamy of correlations. Bell states supplies the standard two-qubit examples.
Three labels that are often conflated have different trust boundaries:
| Family | Untrusted component | Still assumed |
|---|---|---|
| Entanglement based | Source, if allowed by the proof | Characterized local measurements |
| MDI-QKD | Relay measurement | Characterized endpoint sources |
| DI-QKD | Source and measurement internals | Private settings and isolated laboratories |
All three require authentication, suitable randomness and a finite-statistics analysis. Bell violation is not required for every entanglement-based QKD proof. Conversely, observing some Bell-inequality violation is not automatically a complete device-independent implementation proof. Detection, locality, memory, input independence and finite-size assumptions all enter.
Parameter Estimation and Abort
Section titled “Parameter Estimation and Abort”Alice and Bob publicly reveal a randomly selected subset of outcomes or use designated test settings. From those data they construct a confidence region for quantities such as yields, bit-error rates, phase-error rates, or Bell parameters. The key-generating sample remains unrevealed.
For a simple independent Bernoulli model, Hoeffding’s inequality illustrates the statistical logic:
where is an error frequency from test trials and is the underlying mean. Actual QKD analyses may sample without replacement, use random stopping times, estimate several photon-number sectors, or defend against coherent attacks. They therefore use bounds matched to the protocol rather than inserting this illustrative expression blindly.
The bit-error rate quantifies disagreement in the key basis. A phase-error rate is usually a counterfactual or complementary-basis quantity that controls secrecy; it need not equal the observed bit-error rate unless symmetry or another proof step establishes the relation. A valid proof explains how test data bound the phase-error quantity with failure probability .
Loss is not automatically evidence of security and cannot simply be discarded from the threat model. Eve may replace a lossy channel, suppress selected signals, or exploit efficiency mismatch. Detection events, no-clicks, double clicks, basis dependence, and postselection rules must be included in the model. If the resulting confidence region permits no positive key length, Alice and Bob abort.
Reconciliation and Error Verification
Section titled “Reconciliation and Error Verification”After sifting and testing, Alice and Bob hold correlated strings and . Information reconciliation sends parity data or another error-correcting transcript over the authenticated public channel so Bob can infer Alice’s string. One-way methods and interactive two-way methods have different leakage and proof implications.
The transcript is visible to Eve. A security analysis tracks an upper bound
on the information revealed by reconciliation, including disclosed syndromes and any other correlated messages covered by the chosen definition.
Reconciliation may fail silently. Write the two candidate strings as and . To verify agreement, choose a fresh random hash from a two-universal family with -bit output, independently of the already fixed candidate strings. For any unequal strings, the collision probability is at most . Thus
for the candidate strings before hashing, apart from separately counted authentication errors. A mismatch causes an abort. The verification seed may be public, but the strings must not be adaptively changed after it is known. A fixed checksum has no corresponding guarantee against deliberately chosen collisions. The tag can reveal up to bits and must be included in the secrecy calculation. This comparison checks equality; it does not authenticate the sender by itself.
Privacy Amplification
Section titled “Privacy Amplification”Even an agreed string can be partially known to Eve. Privacy amplification compresses it with a fresh independent random choice of a two-universal hash:
The seed identifying is public. Independence from the input and Eve’s pre-existing information is essential; secrecy of the seed is not.
Let contain the public discussion through verification, before this seed is chosen. On the normalized accepted state, suppose a proof supplies
Conditional min-entropy measures unpredictability against optimal quantum guessing; smoothing allows a nearby state within a specified small distance. With purified-distance smoothing, a sufficient quantum leftover-hash bound is
Here the final transcript in includes the hash seed (Tomamichel et al., 2011). The proof must also handle any probability that its entropy estimate fails. One may instead use subnormalized accepted states, but the normalization, smoothing and acceptance factors must be consistent throughout; they cannot be exchanged silently.
The exponential has a useful interpretation: removing two more key bits halves the hash contribution. For a target contribution , it is sufficient to require
For example, a 256-bit sacrifice makes this contribution under the displayed convention. Smoothing and parameter-estimation errors can still dominate the total error. Hashing cannot remove an unmodeled side channel unless the entropy bound already accounts for it.
Key length and rate
Section titled “Key length and rate”For independent and identically distributed classical–classical–quantum data and one-way direct reconciliation, the Devetak–Winter theorem (2005) gives an achievable rate bound:
The first term is Alice’s uncertainty from Eve’s viewpoint; the second is the information Bob lacks and reconciliation must supply. This is not a universal finite-key formula. A protocol proof must justify the state, direction of reconciliation, attack reduction, and observed-parameter constraints used to evaluate the entropies.
For a finite block, one can first bound entropy before reconciliation and then bound the loss caused by its public messages. If is an appropriate smooth min-entropy lower bound before those messages, a sufficient choice has the form
where bounds reconciliation disclosure, counts the verification tag and is the hash margin. This assumes the entropy theorem already handles parameter estimation and acceptance with the chosen smoothing and failure probabilities. Those probabilities are not all interchangeable with subtracting a fixed number of bits. Variable-length or interactive transcripts require a leakage bound justified for their actual structure (Tomamichel and Leverrier, 2017).
Alternatively, condition the entropy on the entire pre-hash transcript, as in above, and do not subtract the same disclosure again. An independent public seed has no automatic one-bit-per-seed-bit leakage cost; a correlated parity tag can have such a cost.
For example, suppose the justified bound is bits, with reconciliation bits, a 64-bit verification tag and a 256-bit hash margin. Then
Reserving another 256 output bits to replenish authentication leaves at most net new bits. This is a calculation given a proven entropy bound, not a prediction for a particular optical link.
Bits per sifted signal, per transmitted pulse and per second have different denominators. A rate comparison must include detection and sifting fractions, block duration, finite-key penalties and authentication consumption. Distance alone does not determine the rate: optical loss, noise, detector behavior and the chosen acceptance rule also matter.
Authentication Is Required
Section titled “Authentication Is Required”Without authentication, Eve can mount a man-in-the-middle attack: she runs one QKD session while pretending to be Bob to Alice and another while pretending to be Alice to Bob. Each session may show excellent quantum statistics, yet Eve shares a separate key with each endpoint and can relay or alter later traffic.
Information-theoretic message authentication can be built from universal hashing, as in Wegman–Carter constructions (1981), using a short pre-shared secret. Successful QKD rounds can replenish consumed authentication material and expand the remaining key pool. Precise key-recycling claims depend on the authentication construction and whether the run accepts.
The classical discussion must be authentic but may be public. Encrypting basis announcements or reconciliation data is unnecessary for secrecy if those messages are already included in . Integrity without endpoint identity is also insufficient: Alice must know that the authenticated peer is Bob.
One may bootstrap a first session with post-quantum digital signatures or another computational credential. That is a legitimate hybrid design, but its initial authentication then has a computational security assumption. The long-term claim must state whether later sessions retain, replace, or continue to depend on that assumption.
Implementation Security
Section titled “Implementation Security”A proof describes how devices prepare states, choose settings and report outcomes. Hardware must satisfy that description. A few examples show why the distinction matters:
- Multiphoton weak coherent pulses require photon-number analysis, commonly through decoy states, with justified phase and intensity assumptions.
- Detector blinding or efficiency mismatch can invalidate a trusted measurement model. MDI-QKD moves the relay measurement outside that trusted model; it retains assumptions about endpoint sources (Lo, Curty and Qi, 2012).
- Back-reflected light or an unintended spectral mode can reveal settings. Optical isolation and source characterization must bound such leakage before it can enter an entropy estimate.
- Predictable random choices or communication from a laboratory to Eve can defeat the model even in a device-independent protocol.
The same observed error rate can therefore support different key bounds under different device assumptions. Neither a low error rate nor a single countermeasure establishes security by itself. Eve can also block all signals: secrecy does not guarantee availability.
From a Link to a Secure Application
Section titled “From a Link to a Secure Application”QKD supplies key material to applications. The endpoints still need authenticated identities, protected key storage, synchronized use and protection against reuse. In a trusted-node network, intermediate nodes may handle the end-to-end key; compromising one can expose it. A quantum repeater aims to distribute entanglement across a different trust arrangement and is not simply another name for a trusted relay.
A one-time pad gives information-theoretic confidentiality only when a sufficiently secret key is used once and is as long as the message. It also needs message authentication because the pad alone is malleable. Using QKD key bits with a computational cipher instead retains that cipher’s computational assumptions. The composable key definition lets these later uses inherit a quantified additional error; it does not prove the later construction correct.
QKD and post-quantum cryptography
Section titled “QKD and post-quantum cryptography”Post-quantum cryptography uses classical algorithms whose security rests on computational assumptions and runs over ordinary digital channels. QKD uses specialized quantum signals and a physical security model; it still requires authentication. A hybrid can combine these resources, but its security depends on how they are composed. The useful comparison concerns a particular threat model and communication task, rather than an unconditional claim that either approach replaces the other.
Exercises
Section titled “Exercises”1. Compose correctness and secrecy
Section titled “1. Compose correctness and secrecy”Suppose a protocol is correct and secret. Give a valid upper bound on its overall soundness error. What does this number not say?
Solution
By the triangle or hybrid argument used to replace the real resource first by a matching-key resource and then by a uniform secret-key resource,
This does not bound the probability of honest abort, guarantee availability, describe implementation side channels, or certify the encryption application that later consumes the key.
2. Show why authentication cannot be omitted
Section titled “2. Show why authentication cannot be omitted”Construct a man-in-the-middle attack against a QKD protocol whose classical channel is public and integrity-protected only by unauthenticated checksums.
Solution
Eve terminates Alice’s quantum and classical traffic and initiates a separate session with Bob. She presents herself as Bob to Alice and as Alice to Bob. Checksums detect accidental corruption but do not bind either transcript to an identity, so Eve can generate valid checksums for both sessions.
Alice finishes with a key shared with Eve, while Bob finishes with a different key shared with Eve. Eve can decrypt, alter, and re-encrypt later traffic between the two sessions. Quantum error tests can pass because Eve is a legitimate endpoint in each separate run.
3. A rare accepted key
Section titled “3. A rare accepted key”A protocol accepts with probability . When it accepts, Alice and Bob share one uniform bit , but Eve holds an exact classical copy. Find and the accepted contribution to the full secrecy distance.
Solution
Conditioned on acceptance, the joint distribution of is on and , and zero on and . The ideal independent distribution is on all four outcomes. Since these states are classical, trace distance is total variation distance:
The full-protocol distance is small because the accepted branch is rare. Within that branch, Eve knows the bit perfectly. This demonstrates why the weighted security definition cannot be read as the same bound on the normalized accepted state. The protocol is also practically useless because it almost always aborts.
4. Illustrative parameter bound
Section titled “4. Illustrative parameter bound”Under an independent Bernoulli model, test bits have observed error frequency . Use Hoeffding’s inequality to find such that the failure probability for this upper confidence bound is at most .
Solution
Set
Then
With the stated confidence, the illustrative upper bound is
This calculation is not automatically valid for a QKD sample drawn without replacement or for a non-i.i.d. attack; the protocol must use the statistical theorem matching its sampling procedure and adversary reduction.
5. Choose a finite key length
Section titled “5. Choose a finite key length”A proof gives a smooth min-entropy bound bits before reconciliation, with parameter estimation and acceptance already handled. Reconciliation leaks at most bits, verification costs bits, and the privacy-amplification margin is bits. Find the largest output length allowed by this simplified bound. If output bits replenish authentication, what is the net expansion?
Solution
The output length obeys
After reserving bits for authentication, the net expansion is
bits. A real proof may place some transcript terms inside the conditional min-entropy and may contain additional finite-size penalties.
6. Privacy-amplification margin
Section titled “6. Privacy-amplification margin”Ignore smoothing and convention-dependent prefactors. If the reconciled string has conditional min-entropy at least bits and Alice extracts bits, estimate the leftover-hash contribution
Solution
The entropy sacrifice is bits, so
The extractor contribution is therefore extremely small. The total secrecy error may still be dominated by smoothing or parameter estimation; composing with imperfect authentication adds its own security error.
7. Interpret the Devetak–Winter terms
Section titled “7. Interpret the Devetak–Winter terms”Suppose a justified asymptotic model gives
bits per sifted signal. What one-way achievable rate follows, and why is it not yet an experimental throughput?
Solution
The expression gives
secret bits per sifted signal in the stated asymptotic model. It omits finite-block penalties, sifting and detection probabilities, authentication cost, clock rate, dead time, loss, postselection, and the distinction between sifted signals and transmitted pulses. Those are needed to convert the entropy rate into net bits per second.
8. Compose QKD with message protection
Section titled “8. Compose QKD with message protection”Alice and Bob obtain a -bit QKD key. Compare using it for a -bit one-time pad with using 256 bits as an AES key. State the additional requirements in each case.
Solution
For a one-time pad, the full -bit key can encrypt one message of the same length with information-theoretic confidentiality, provided the key is sufficiently uniform, never reused, synchronized, erased appropriately, and combined with a secure message-authentication mechanism. The pad alone is malleable.
Using 256 bits as an AES key allows much more data to be processed, but confidentiality rests on the computational security and correct mode of operation of AES. An authenticated-encryption construction, nonce discipline, endpoint security, and key lifecycle are still required. In neither case does the QKD layer by itself protect the application.
References
Section titled “References”- C. H. Bennett and G. Brassard, “Quantum cryptography: Public key distribution and coin tossing,” in Proceedings of the IEEE International Conference on Computers, Systems and Signal Processing, Bangalore, 175–179 (1984); reprinted in Theoretical Computer Science 560, 7–11 (2014), doi:10.1016/j.tcs.2014.05.025.
- C. H. Bennett, G. Brassard, and N. D. Mermin, “Quantum cryptography without Bell’s theorem,” Physical Review Letters 68, 557–559 (1992), doi:10.1103/PhysRevLett.68.557.
- I. Devetak and A. Winter, “Distillation of secret key and entanglement from quantum states,” Proceedings of the Royal Society A 461, 207–235 (2005), doi:10.1098/rspa.2004.1372.
- A. K. Ekert, “Quantum cryptography based on Bell’s theorem,” Physical Review Letters 67, 661–663 (1991), doi:10.1103/PhysRevLett.67.661.
- H.-K. Lo, M. Curty, and B. Qi, “Measurement-device-independent quantum key distribution,” Physical Review Letters 108, 130503 (2012), doi:10.1103/PhysRevLett.108.130503.
- C. Portmann and R. Renner, “Cryptographic Security of Quantum Key Distribution,” arXiv:1409.3525 (2014).
- C. Portmann and R. Renner, “Security in quantum cryptography,” Reviews of Modern Physics 94, 025008 (2022), doi:10.1103/RevModPhys.94.025008.
- M. Tomamichel and A. Leverrier, “A largely self-contained and complete security proof for quantum key distribution,” Quantum 1, 14 (2017), doi:10.22331/q-2017-07-14-14.
- M. Tomamichel, C. Schaffner, A. Smith, and R. Renner, “Leftover Hashing Against Quantum Side Information,” IEEE Transactions on Information Theory 57, 5524–5535 (2011), doi:10.1109/TIT.2011.2158473.
- M. N. Wegman and J. L. Carter, “New hash functions and their use in authentication and set equality,” Journal of Computer and System Sciences 22, 265–279 (1981), doi:10.1016/0022-0000(81)90033-7.